Cloudflare Tunnel vs Tailscale: Which to Use?
People compare Cloudflare Tunnel and Tailscale as interchangeable, but they point in opposite directions: Tunnel is outbound ingress to the public internet, Tailscale is a private WireGuard mesh for your own devices. Here's which to pick, when, and how they work together, with current pricing.
TL;DR
- Cloudflare Tunnel (
cloudflared) is an outbound-only reverse tunnel that publishes a private service to Cloudflare's edge — usually to the public internet, optionally gated by Cloudflare Access. It is an ingress tool. No inbound ports opened. - Tailscale is a private mesh VPN built on WireGuard that links your own devices into one flat network (a tailnet). It is a private-access tool — the service stays reachable only to devices you authorize.
- Verdict: Use Cloudflare Tunnel to expose a service to people who are not on your network. Use Tailscale for private access to your own machines from your own devices. They work well together.
- Pricing: Cloudflare Zero Trust is free for 50 users, then $7/user/mo. Tailscale is free for up to 6 users (personal), then $8/user/mo.
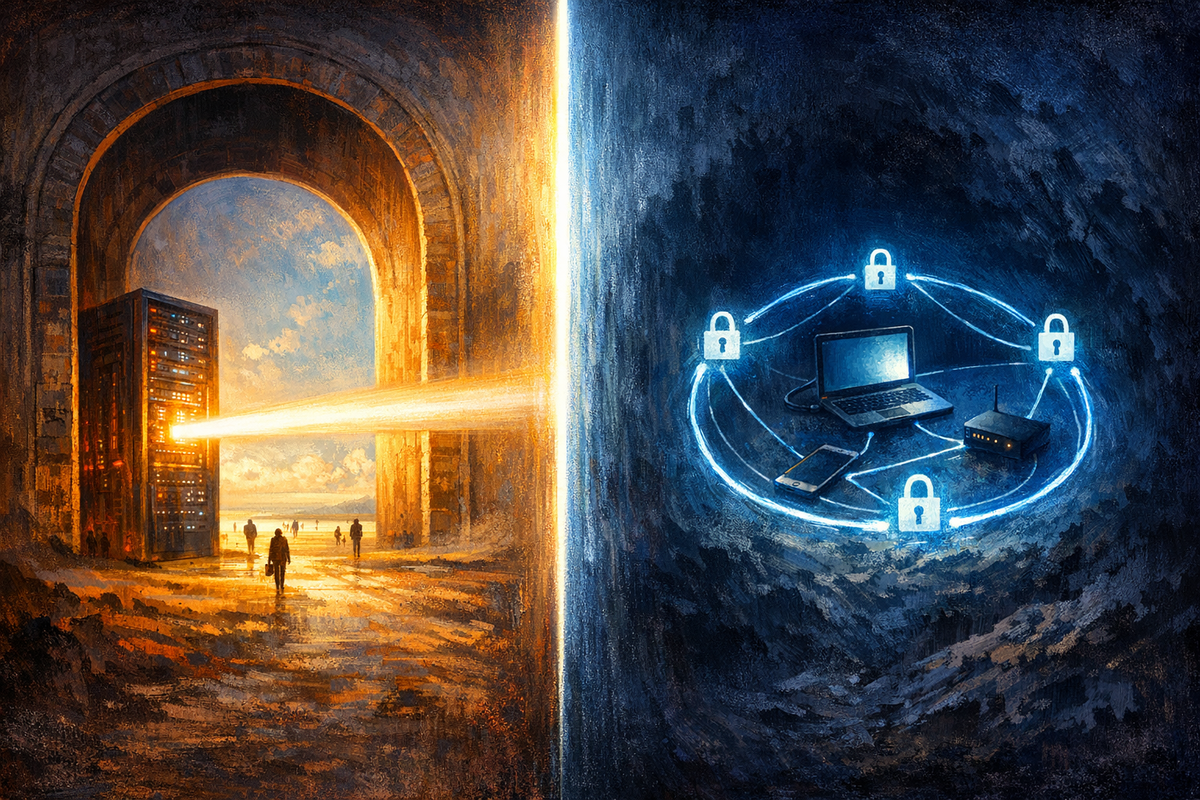
Cloudflare Tunnel and Tailscale are not two ways to do the same job. Cloudflare Tunnel exposes a private service outward — pick it when outside users, clients, or webhooks need to reach something without you opening a port. Tailscale connects your own devices into a private network — pick it for homelab, remote dev, or SSH to machines only you should reach. Most teams end up running both.
What is Cloudflare Tunnel?
Cloudflare Tunnel is a daemon, cloudflared, that proxies traffic from the Cloudflare network to your origins. It makes a persistent outbound connection to Cloudflare's edge, so your service becomes reachable through Cloudflare without a public IP, port forwarding, or inbound firewall rules.
The daemon connects out on port 7844 — TCP (HTTP/2) and UDP (QUIC) — to Cloudflare's regional tunnel endpoints. Cloudflare's own firewall guidance is to allow cloudflared egress and block all ingress. Nothing reaches your box except replies on connections it opened.
By default a tunnel publishes a hostname to the public internet. To restrict who can reach it, you layer Cloudflare Access (part of Cloudflare's Zero Trust suite) in front for authentication. cloudflared is open source under Apache-2.0.
What is Tailscale?
Tailscale is a private mesh VPN built on WireGuard — specifically the userspace wireguard-go implementation. It joins your devices into a single flat network called a tailnet, where each node talks to the others over peer-to-peer encrypted tunnels.
A central coordination server handles only the control plane: it exchanges public keys and device locations. It carries no user traffic, and private keys never leave the device. For connectivity it uses NAT traversal (STUN/ICE) to punch direct connections, falling back to DERP relays when UDP is blocked — and those relays forward already-encrypted packets they cannot read.
Access is governed by ACLs distributed to every node, and authentication is delegated to your SSO provider (OAuth2, OIDC, or SAML). Features like MagicDNS and Tailscale SSH sit on top. The service stays private to the devices you authorize — it is never exposed to the public internet unless you deliberately add a feature like Funnel.
If you have landed here from WireGuard itself, our Tailscale vs WireGuard comparison covers how the managed mesh is built on the raw protocol.
Cloudflare Tunnel vs Tailscale: the core difference
The comparison trips people up because the two tools point in opposite directions.
Cloudflare Tunnel is ingress. It takes something private and makes it reachable from outside — typically by anyone on the internet, optionally behind an auth gate. The question it answers is "how do strangers reach my service safely?"
Tailscale is a private mesh. It makes your machines reachable to each other and to you, and to nobody else. The question it answers is "how do I reach my own machines from anywhere?"
That is why a raw Tunnel and Tailscale are not true substitutes. The honest apples-to-apples comparison to Tailscale's private access is Cloudflare Access + Tunnel together (Cloudflare's Zero Trust model), not cloudflared on its own. That same ZTNA framing is what separates the dedicated secure-access products in our Twingate vs Tailscale breakdown.
How do they compare on setup, security, and pricing?
Both avoid open inbound ports and both end-to-end encrypt traffic, but they differ on who can reach the service and who sees the plaintext.
Setup: Tunnel needs a Cloudflare account, a domain on Cloudflare, and the cloudflared daemon on the origin. Tailscale needs the client on every device plus an SSO login — no domain, no DNS changes.
Security: With Tunnel, TLS terminates at Cloudflare's edge, so Cloudflare can see decrypted traffic (the trade-off for its WAF, DDoS protection, and caching). With Tailscale, traffic is end-to-end between your nodes; the coordination server and DERP relays never hold plaintext or private keys. If your concern is governing employee access to internal apps, that is the same lane as Zscaler vs Netskope.
Pricing (verify live — pricing changes): Cloudflare's Zero Trust plan, which adds Access in front of a tunnel, is free for up to 50 users, then $7/user/mo pay-as-you-go. Tailscale's pricing is free for up to 6 users on the personal plan, then $8/user/mo (Standard) or $18/user/mo (Premium).
| Dimension | Cloudflare Tunnel (+ Access) | Tailscale |
|---|---|---|
| What it is | Outbound reverse tunnel to Cloudflare's edge | Mesh VPN over WireGuard |
| Direction | Ingress — publishes a service outward | Mesh — connects your own devices |
| Underlying tech | Cloudflare global edge network | WireGuard (wireguard-go) + DERP relays |
| Who can reach the service | Public internet (optionally gated by Access) | Only devices you authorize on the tailnet |
| Auth model | Cloudflare Access policies (Zero Trust) | Tailnet ACLs + your SSO (OIDC/SAML) |
| Open source | cloudflared — Apache-2.0 |
Clients open source; self-host control via Headscale (BSD-3-Clause) |
| Free tier | Zero Trust free for 50 users | Personal: free, up to 6 users, unlimited devices |
| Paid entry price | $7/user/mo (pay-as-you-go) | $8/user/mo (Standard); $18/user/mo (Premium) |
| Best for | Publishing sites, APIs, webhooks to outside users | Private access to your own machines/services |
When should you use each?
Homelab / self-hoster: If you want to reach your own services (Home Assistant, a NAS, SSH) from your phone or laptop and nobody else should see them, use Tailscale — it is the cleaner fit and free for personal use. If you want to publish something to the public (a blog, a shared app, a webhook target) without opening ports, use Cloudflare Tunnel. Many self-hosters run both.
Solo dev: Use Tailscale to SSH into remote dev boxes or GPU machines and hit internal dashboards. Use Cloudflare Tunnel to expose a local dev server for a client demo or to receive webhooks from a third party.
Platform / security team: If the job is ZTNA for employees — private access to internal apps with SSO and policy — compare Tailscale against Cloudflare Access + Tunnel, not raw Tunnel. Cloudflare's model routes through its edge and adds WAF/DLP; Tailscale keeps traffic peer-to-peer and end-to-end encrypted. If the job is publishing a public service behind Cloudflare's security stack, that is Tunnel's lane, full stop.
Can you use Cloudflare Tunnel and Tailscale together?
Yes, and it is a common, sensible pattern. They cover different directions, so they compose cleanly.
A typical split: Tailscale for everything private — admin access, SSH, internal dashboards reachable only from your devices — and Cloudflare Tunnel for the one or two things the public actually needs to hit. You get Cloudflare's edge protection on the public surface and a private mesh for everything else, with no inbound ports open either way.
Frequently Asked Questions
What is the difference between Cloudflare Tunnel and Tailscale?
Cloudflare Tunnel is an outbound reverse tunnel that publishes a private service to Cloudflare's edge, usually for the public internet. Tailscale is a private mesh VPN on WireGuard that connects your own devices to each other. One is ingress; the other is private peer-to-peer access.
Is Cloudflare Tunnel or Tailscale more secure?
Both encrypt traffic and need no open inbound ports. The difference is trust. With Tunnel, traffic decrypts at Cloudflare's edge, which enables its WAF and DDoS protection but means Cloudflare sees plaintext. With Tailscale, traffic stays end-to-end between your nodes; the control server never holds keys or plaintext.
Can I use Cloudflare Tunnel and Tailscale together?
Yes. They solve opposite problems, so they layer well. Teams commonly use Tailscale for private access to their own machines and Cloudflare Tunnel to expose the specific services outside users need — both without opening any inbound ports.
Is Cloudflare Tunnel free?
The cloudflared daemon is free and open source (Apache-2.0), and Cloudflare Tunnel itself has no separate charge. Cloudflare's Zero Trust plan, which adds Access policies in front of a tunnel, is free for up to 50 users, then $7/user/mo pay-as-you-go.
Which is better for self-hosting?
For reaching your own services privately, Tailscale is usually the better fit and free for personal use. For publishing something to the public without port forwarding, Cloudflare Tunnel wins. Self-hosters who want full control can run Headscale, an open-source Tailscale control server.
Editor's note — sources: cloudflared on GitHub (github.com/cloudflare/cloudflared — Apache-2.0, daemon description); Cloudflare Tunnel firewall guidance (developers.cloudflare.com — port 7844 TCP/UDP, block-all-ingress); Tailscale: How Tailscale works (tailscale.com/blog/how-tailscale-works — WireGuard/wireguard-go, coordination server, DERP, ACLs, SSO); Cloudflare Zero Trust plans (cloudflare.com/plans/zero-trust-services — free 50 users, $7/user/mo); Tailscale pricing (tailscale.com/pricing — free up to 6 users, $8/$18 per user/mo); Headscale on GitHub (github.com/juanfont/headscale — open-source Tailscale control server, BSD-3-Clause).