Datadog vs Splunk: 2026 Pricing and Verdict
Both start at $15 per host per month. What separates Datadog and Splunk in 2026 is quote-only pricing, SIEM depth and where Cisco is taking the platform.
TL;DR
- Entry list prices are identical. Datadog Infrastructure Pro starts at $15 per host per month on annual billing; Splunk Observability Cloud Infrastructure also starts at $15 per host per month. The divergence happens above the entry tier.
- Datadog publishes almost everything. Splunk mostly does not. Splunk Cloud Platform, Splunk Enterprise, Enterprise Security and ITSI are all quote-only.
- Cisco closed the ~$28bn Splunk deal in March 2024. Cisco's Observability line booked $275m in Q4 FY2026, up 6%. Datadog booked $1.12bn in Q2 2026 alone, up 36%.
- Verdict: Datadog for cloud-native observability and AI-era application monitoring. Splunk for SIEM, regulated log retention, on-premises and air-gapped. The SIEM is the part that does not migrate.
Datadog vs Splunk comes down to what you are actually buying. Datadog is a cloud-delivered observability and security platform with published per-host, per-GB and per-event list prices. Splunk, owned by Cisco since March 2024, is a machine-data and SIEM platform with mostly quote-only pricing. Datadog wins on cloud-native APM. Splunk wins on log-heavy security.
Worth saying up front: almost every comparison of these two on page one of Google is published by an observability vendor selling a third option, by Splunk itself, or by an affiliate site earning a referral. Edgewisely sells neither product and takes no referral fee. Every number below comes from a vendor pricing page, newsroom post or earnings release, checked on 29 September 2026.
What is the difference between Datadog and Splunk?
Datadog began as infrastructure monitoring and grew into APM, logs, real user monitoring, security and AI observability on one SaaS backbone. Splunk began as a search engine for machine data and grew into the dominant enterprise SIEM.
That origin still shapes both products.
Datadog assumes your telemetry is metrics-and-traces-first and prices per host. Splunk assumes it is log-and-event-first and prices by how much data you ingest or how much compute you burn searching it.
Splunk also ships where Datadog historically could not: self-managed, private cloud and air-gapped. Datadog narrowed that gap in 2026 with Bring Your Own Cloud, for deploying inside customer environments, but air-gapped remains Splunk territory.
| Datadog | Splunk (Cisco) | |
|---|---|---|
| Core strength | Cloud-native APM, infrastructure, unified platform | Machine-data search, SIEM, compliance retention |
| Primary metering | Per host, per GB ingested, per event indexed | Ingest volume, workload, activity or entity |
| Deployment | SaaS; Bring Your Own Cloud | SaaS, self-managed, private cloud, air-gapped |
| Query language | Tag-based filters, no dedicated DSL required | SPL — steep curve, very powerful |
| SIEM | Cloud SIEM, a separate SKU | Enterprise Security, market-leading |
| Free tier | Up to 5 hosts | Observability Cloud Free Edition, up to 15 hosts |
| Published list pricing | Extensive | Observability and AppDynamics only |
Splunk vs Datadog pricing: what each vendor actually publishes
Here is the real answer. Datadog tells you what most things cost before you talk to a salesperson. Splunk tells you what observability costs and makes you call for everything else.
List prices below, annual commitment, from Datadog's pricing page and Splunk's pricing page.
| Component | Datadog (list, annual) | Splunk (list, annual) |
|---|---|---|
| Infrastructure monitoring | $15/host/mo (Pro); $23 (Enterprise) | $15/host/mo (Observability Cloud Infrastructure) |
| APM with infrastructure | $31/host/mo | $60/host/mo (App & Infra) |
| Full stack including RUM | APM Enterprise from $40/host/mo, RUM billed separately | $75/host/mo (End-to-End) |
| Log ingestion | $0.10 per ingested or scanned GB | Quote-only |
| Log indexing | $1.70 per million log events | Quote-only |
| Agent / LLM observability | Agent Observability, billed via AI Credits | From $100/mo per 1.2m spans |
| Legacy / on-prem APM | Not offered | Splunk AppDynamics from $6/vCPU/mo; Enterprise Edition from $50/host/mo |
| On-call | Included in platform SKUs | Splunk On-Call from $5/user/mo, up to 10 seats |
| SIEM | Cloud SIEM, separate SKU on top of log ingestion | Enterprise Security — quote-only |
| Core data platform | Not offered | Splunk Cloud Platform / Enterprise — quote-only |
Three things buyers consistently miss.
Datadog's per-host price is the floor, not the bill. Containers beyond your allotment bill separately, as do custom metrics, indexed spans and retention tiers. The $15 line is where the bill starts forming, not where it lands.
Splunk's quote-only surface is where the money is. Observability Cloud is transparently priced. The Splunk Platform, Enterprise Security and ITSI — the products most Splunk shops actually spend on — are not.
Cisco telemetry gets a discount inside Splunk. Splunk's pricing page states that eligible Cisco telemetry ingests at a 0.5x weighted rate. If you run Cisco networking gear at scale that materially changes the arithmetic, and no competitor comparison page will price it for you.
What changed after Cisco acquired Splunk?
Cisco completed the acquisition on 18 March 2024 at $157 per share, roughly $28 billion. Two and a half years on, the integration is visible in the product names.
AppDynamics is now Splunk AppDynamics. Splunk On-Call, Observability Cloud and ITSI all sit under the Splunk Observability banner. Check any product name against the live page before you put it in a procurement document, because several have moved.
The commercial picture is more mixed than the product picture. In Cisco's Q4 FY2026 results, the Observability category delivered $275 million in the quarter, up 6%, against total company revenue of $17.3 billion, up 18%. Splunk revenue is split across Cisco's Security and Observability lines, so that figure is not all of Splunk, but it is the closest public read on the observability business.
For contrast, Datadog reported Q2 2026 revenue of $1.12 billion, up 36% year over year, with about 4,720 customers at $100,000 or more in annual recurring revenue. Datadog books more revenue in one quarter than Cisco's entire Observability line books in a year, and grows roughly six times faster.
Read that as momentum, not as product quality. It does tell you where roadmap velocity is likely to come from.
Datadog vs Splunk observability: AI and agent monitoring in 2026
Both vendors shipped serious agent observability this year. This is the newest axis of comparison and the one every older ranking page misses.
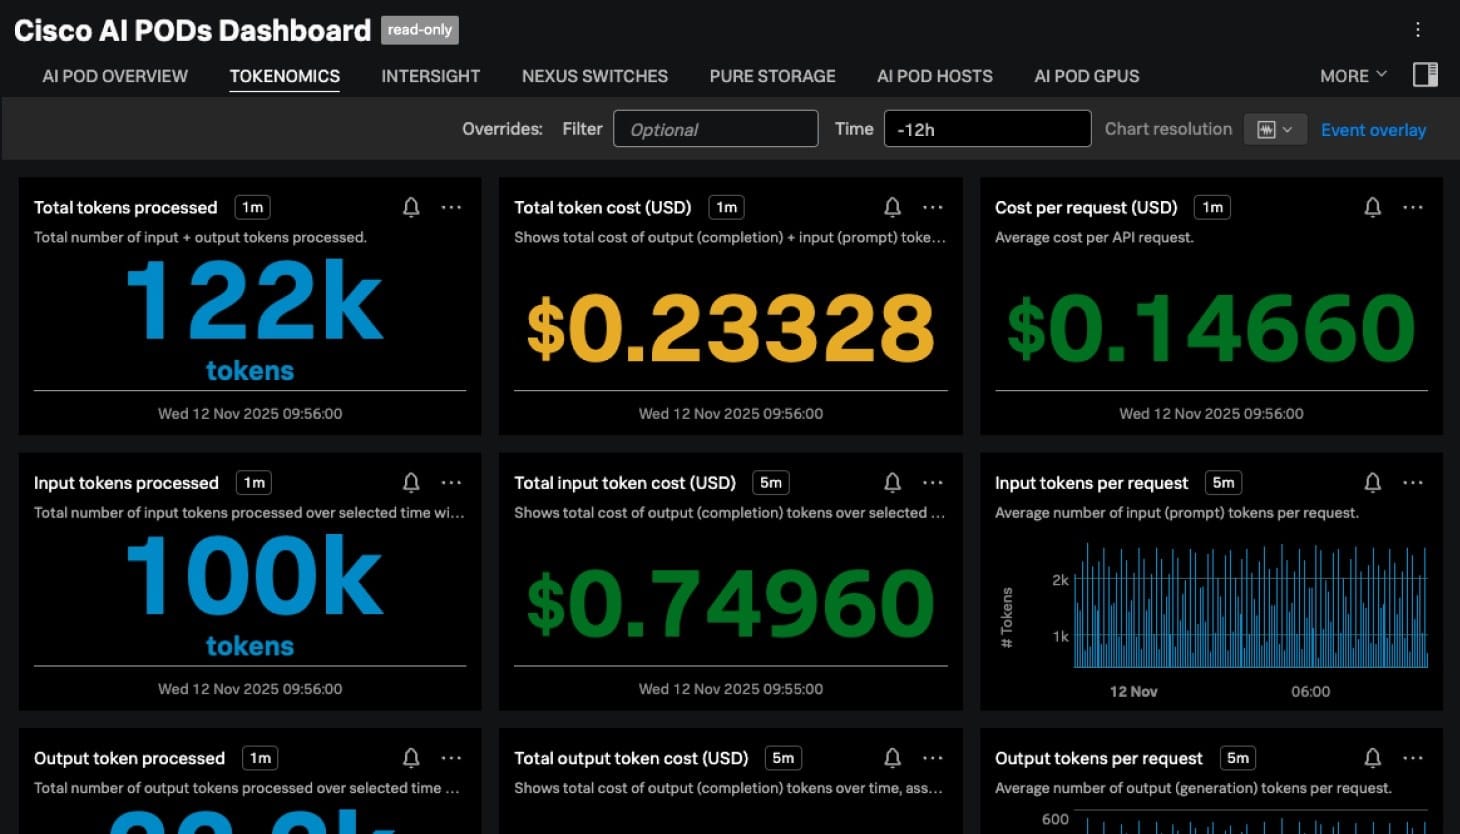
Splunk announced a substantial refresh at .conf26 on 15 September 2026. Splunk Agent Observability, built on Cisco's Galileo acquisition, adds a Tokenomics module that tracks token spend across AI agents and across employee coding agents including Claude Code, Codex and Cursor. Evaluations and runtime guardrails run on purpose-built small models, which is what makes scoring all production traffic affordable rather than sampling it. Also new: Observability Studio, a Network Intelligence App pulling Cisco topology into Splunk, and Cisco AI POD for Splunk, which brings Splunk AI to on-premises and air-gapped environments.
One currency note. That announcement introduced new Essentials and Premier editions for Observability Cloud, but Splunk's live pricing page still lists the older Infrastructure, App & Infra and End-to-End tiers. Ask your rep which SKU structure your quote is written against.
Datadog consolidated its LLM observability product into Agent Observability and shipped Bits AI for autonomous incident detection, investigation and remediation, billed through a separate AI Credits SKU. It also shipped AI Guard for prompt injection and poisoning protection.
Functionally these are converging fast. Splunk's differentiator is that agent traces sit next to network topology and GPU telemetry. Datadog's is that the remediation loop is further along toward autonomy. If you are choosing specifically for LLM tracing rather than whole-stack observability, our Langfuse vs LangSmith comparison covers the lighter-weight options.
What this means for you
If you are a startup or cloud-native platform team. Datadog. Published pricing, faster onboarding, no SPL learning curve, and the strongest cloud-native APM. Budget above the $15 line — containers, custom metrics and log indexing are where the bill actually forms. Set spend alerts in week one. Our observability and APM tools roundup covers the cheaper alternatives if neither of these fits.
If you run a security operations centre. Splunk, and it is not close. Enterprise Security plus SOAR and UEBA is a deeper stack than Datadog Cloud SIEM. Accept that you will negotiate rather than read a price. Our SIEM tools comparison puts Splunk against the rest of that field.
If you are a Cisco networking shop. Splunk. The 0.5x weighted ingest rate on eligible Cisco telemetry, plus the Network Intelligence App, are real economics no third-party comparison will model for you.
If you have regulated, air-gapped or sovereignty requirements. Splunk. Cisco AI POD for Splunk runs Splunk AI on-premises. Datadog's Bring Your Own Cloud narrows this gap but does not reach air-gapped.
If you are running both today. Most large enterprises are. Consolidating usually means moving observability to Datadog and keeping Splunk for SIEM and compliance retention. Pilot both free tiers first: Datadog covers 5 hosts, Splunk Observability Cloud Free Edition covers 15.
If cost control is the whole problem. Neither vendor is cheap and both are known for bill shock. Splunk's Ingest and Edge Processors filter before indexing, and Cloud Flex lets you reallocate committed spend across the portfolio. Datadog's Flex Logs separates cheap storage from expensive indexing. Use these. They are the difference between a predictable bill and a bad quarter.
Frequently Asked Questions
Is Datadog cheaper than Splunk?
Not reliably. Entry list prices are identical: Datadog Infrastructure Pro and Splunk Observability Cloud Infrastructure both start at $15 per host per month billed annually. Datadog's log ingestion lists at $0.10 per GB. Splunk's platform, SIEM and ITSI are quote-only, so total cost depends entirely on negotiated terms.
Can Datadog replace Splunk?
For observability, usually yes. For SIEM and compliance-driven log retention, often no. Datadog Cloud SIEM exists, but Splunk's detection content, SPL queries and regulated-industry deployments are hard to migrate. Datadog's Bring Your Own Cloud narrows the on-premises gap but does not close air-gapped requirements.
What is the difference between Datadog and Splunk?
Datadog is a cloud-delivered observability and security platform priced per host, per GB and per event, strongest on cloud-native APM and infrastructure. Splunk is a machine-data platform built around search and SIEM, sold by Cisco, available as SaaS, self-managed or air-gapped, and priced by ingest, workload or activity.
Is Splunk still worth it after the Cisco acquisition?
Yes, if you are a Splunk SIEM shop or a Cisco networking shop. Cisco is investing: .conf26 shipped agent observability with token-cost tracking and on-premises Splunk AI. Eligible Cisco telemetry ingests at a 0.5x weighted rate. If you are neither, the bundle logic does not apply to you.
Editor's note — sources: Datadog list pricing from Datadog's pricing page; Splunk list pricing, the 0.5x weighted Cisco telemetry ingest rate and the quote-only status of Splunk Cloud Platform, Enterprise Security and ITSI from Splunk's pricing page. Acquisition terms from Cisco's completion announcement (18 March 2024). Cisco Q4 FY2026 Observability revenue of $275m, up 6%, from Cisco's fourth quarter earnings release. Agent observability features from Cisco's .conf26 announcement (15 September 2026). Datadog Q2 2026 revenue of $1.12bn, up 36%, and approximately 4,720 customers at $100k+ ARR are from Datadog's second quarter 2026 results, published 6 August 2026. All figures checked 29 September 2026.